
Cybersecurity . . By Devzin Team
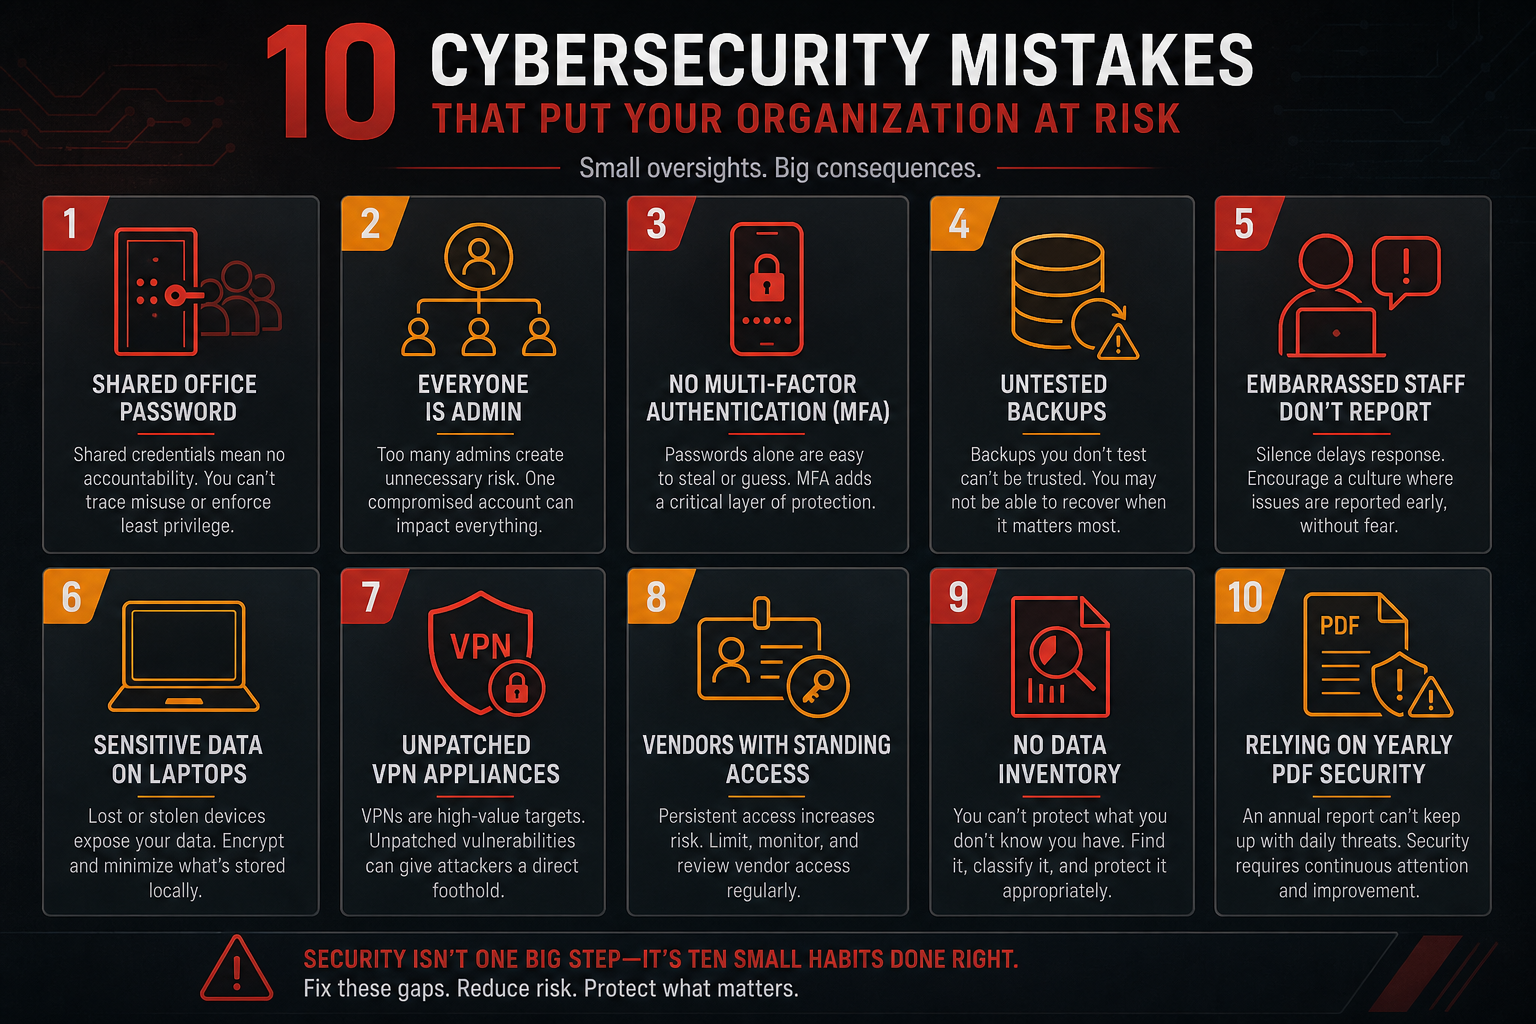
A school office and a five-person company make the same bets: one shared password, a vendor who still has last year’s login, and a backup nobody has opened. Attackers do not need a clever exploit when the door is a reused email password.
The ten we keep seeing
- One shared password for “the office login.”
- Admin rights for everyone because support was busy.
- No MFA on email and cloud consoles.
- Backups that have never been restored.
- Staff who click, then feel too embarrassed to report.
- Production data in uncontrolled laptops and chat tools.
- Unpatched VPN and remote-access tools.
- Vendors with standing access “just in case.”
- No inventory of where customer data lives.
- Security treated as a once-a-year PDF.
This week, not a policy rewrite
- Turn on MFA for email and any admin console
- Name one person who can grant admin — and remove the rest
- Restore a backup once so you know it works
- Write down where customer or student data actually lives
Phishing is how several of these explode — protect against phishing and social engineering. If you build software, start from secure web applications.
FAQ
Are we too small to be a target?
Size is not the filter attackers use. Convenience is. See why small businesses are bigger targets.
If you need software built around a real workflow — not a stack of disconnected tools — see Devzin application development or start a conversation.
